


On this page
AI agents can read company data, call APIs, update systems, and spend money without waiting for another human prompt. AI agent governance determines what they can access, which actions they can take, what they can spend, and who remains accountable for each action.
For action-taking agents, policy alone is not enough. Controls need to operate while the agent is running, before sensitive data leaves, permissions are exercised, or high-impact actions execute.
The gap it closes is widening. IBM's 2026 Cost of a Data Breach Report found that security incidents involving shadow AI more than doubled, from 20% to 43% of breached organizations, and that 92% of organizations with an AI-related breach lacked proper AI access controls. Gartner estimates that 40% of organizations will demote or decommission autonomous agents because of governance gaps identified only after production incidents (Gartner, May 2026, cited by OneTrust).
This guide covers the definition, the risks, the frameworks, and a scoring model for agent risk. It also covers ownership and the criteria that separate governance software that enforces from software that only documents.
What is AI agent governance?
AI agent governance extends AI governance from what a model says to what an agent does. The definition below is the short version; the sections after it explain why agents need their own controls.
Definition: AI agent governance is the set of identity, policy, data, cost, and audit controls that decide what an autonomous AI agent may do on an organization's behalf, enforced each time the agent acts. For every action, it answers four questions: which agent, acting for whom, is allowed to do what, and leaving what record.
Why agents need different controls
- Agents act without prompts: A goal set once can trigger dozens of actions. Controls that only scan the first prompt miss everything the agent decides to do afterward.
- Agents invoke tools and APIs: Each tool call can read records, move money or send email. Every connected tool is a separate permission surface that needs its own scope and log.
- Agents carry context forward: Memory lets an agent reuse what it saw earlier. Poisoned or sensitive context from step one can shape a harmful action at step ten.
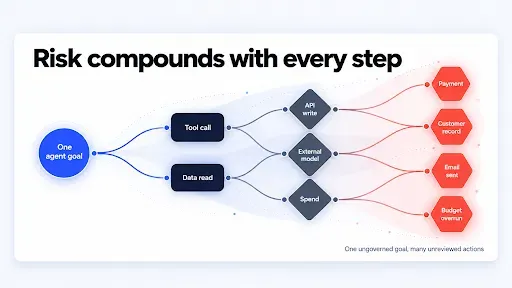
- Risk compounds across steps: A permission that looks harmless alone can combine with others into real damage. Governance has to judge the chain, not only each individual call.
Traditional AI governance vs AI agent governance
| Dimension | Traditional AI governance | AI agent governance |
|---|---|---|
| Scope | Prompts and outputs | Actions, tool calls, and handoffs |
| Control point | Policy documents and periodic review | Runtime, on every request |
| Identity | The user only | The agent plus the user it acts for |
| Risk unit | A single output | A chain of actions |
| Evidence | Usage logs | Identity-attributed action traces |
| Enforcement timing | After review | Inline, before the action runs |
Why ungoverned AI agents create real risk
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
Most agent incidents do not start with an attack. They start with an agent holding more access, budget, or autonomy than its task needed, and no one watching the requests.
- Shadow agents: Teams build or install agents that never reach the security team's inventory. These agents inherit a user's access and run with no owner or review.
- Excessive tool permissions: Agents granted broad API scopes for convenience can call write, delete, or payment endpoints that the task never required.
- Sensitive data exposure: Agents pass customer records, contracts, and identifiers to external models as part of normal work, unless something inspects the request before it leaves.
- Runaway agent spend: Without routing rules, every task hits the most expensive model. Looping agents can burn a month's budget in a weekend with nobody alerted.
- Missing audit evidence: When an auditor asks which agent changed a record and on whose authority, many teams can produce only raw application logs.
- No way to stop an agent mid-task: Teams often discover during an incident that no one knows how to suspend a running agent without taking down the whole application.
- Regulatory exposure: AI laws increasingly expect logging, human oversight, and documented risk assessment. Agents deployed without these controls create gaps that surface during audits.
Stat callout: Only 19% of breached organizations said their governance and security teams coordinate on AI, according to IBM's 2026 Cost of a Data Breach Report. Policy and enforcement drift apart when no one owns both.
Incident proof point: In July 2025, a Replit user reported that its coding agent deleted production database data despite instructions not to make changes. Replit acknowledged the incident and subsequently strengthened development/production separation and agent safeguards.
Agent AI security and governance: how they work together
Security and governance are often bought as separate products, yet agents need both, answering the same question: is this action allowed, and can we prove it? The overlap is larger than most org charts assume.
Security vs governance explained
Agent security defends against adversaries: prompt injection, poisoned tools, and compromised credentials. Agent governance defines what legitimate behavior looks like: who owns an agent, what it may touch, what it may spend, and what evidence it must leave.
In short, security stops the attacker, and governance constrains the insider, including a well-meaning agent that misreads its goal. Teams that need help on the security side can pair governance with data and AI security services.
Where they overlap
Both depend on the same three primitives: a verified identity for every agent, a policy decision before each action, and a tamper-resistant log after it. A team that builds these once serves both the CISO and the compliance lead from one control layer.
OWASP Agentic Top 10 mapping
The table maps six of the OWASP agentic risks to the governance control that addresses each one.
| OWASP risk | What goes wrong | Governance control |
|---|---|---|
| ASI01 Agent goal hijack | Malicious content in an email or file redirects the agent's objective | Policy and scope enforcement |
| ASI02 Tool misuse and exploitation | The agent uses a legitimate tool in an unsafe way | Tool permission controls |
| ASI03 Identity and privilege abuse | The agent acts with more authority than its task needs | SSO and RBAC inheritance |
| ASI06 Memory and context poisoning | Tainted context shapes later decisions | Input inspection and filtering |
| ASI08 Cascading failures | One agent's error spreads through a multi-agent chain | Human escalation and audit |
| ASI10 Rogue agents | An agent operates outside approved behavior while appearing legitimate | Agent registry and ownership |
Source note: The OWASP Top 10 for Agentic Applications 2026 (December 2025) lists ten agent-specific risks, ASI01 to ASI10. The four not mapped above (supply chain, code execution, inter-agent communication, and human-agent trust) mostly need build-time controls.
Core pillars of an AI agent governance framework
A workable framework has seven pillars. Each one closes a specific gap from the risk list above, and together they give auditors, finance, and security the same view of every agent.
- Agent inventory and registry: Every agent, whether built in-house or bought, is recorded with an owner, purpose, connected tools, and risk tier before it can run.
- Identity and access control: Agents inherit the permissions of the user they act for through SSO and role-based access, never holding broader standing credentials of their own.
- Data protection guardrails: Personal data, account numbers, and secrets are detected and masked in prompts and files before any request reaches an external model.
- Policy and scope enforcement: Each agent has a defined domain. Requests outside that domain are declined at runtime instead of being flagged in a report weeks later.
- Model and cost governance: Each role and workload is mapped to an approved model tier, with spend caps and quotas set at department and user level.
- Human oversight and escalation: High-impact actions, such as payments or external email, pause for a named approver, while low-risk actions proceed and are logged.
- Audit trails and evidence: Every request records user, agent, policy decision, model, and cost, giving auditors a structured trace instead of scattered application logs.
Teams that want to benchmark where their program stands today can use the AI governance maturity model alongside these pillars.
The Agent Authority Matrix
Not every agent needs the same level of control. The Agent Authority Matrix scores each agent on four factors, and the total decides how tightly it is governed.
| Factor | Score 1 | Score 2 | Score 3 |
|---|---|---|---|
| Autonomy | Suggests only; a human acts | Acts with human approval | Acts alone |
| Tool reach | Read-only access | Writes to internal systems | Takes external actions or moves money |
| Data sensitivity | Public data | Internal data | Personal, financial, or regulated data |
| Spend exposure | Low-cost model with a cap | Mixed models with a cap | Premium models without a cap |
Governance tier by total score:
- 4 to 6, Monitor: Log every request and review usage monthly. Suited to internal research and summarization agents.
- 7 to 9, Approve: Require human sign-off on high-impact actions and review permissions each quarter.
- 10 to 12, Restrict: Keep scope narrow, cap spend, make escalation mandatory, and re-score after any change.
Worked example: An invoice-matching agent with approved payment drafts, ERP write access, vendor bank data, and capped mixed models scores 9 (2+2+3+2), which puts it in the Approve tier with sign-off above a threshold and a quarterly access review.
Governing agents across their lifecycle
Most governance programs focus on launch day, but agents change after deployment. New tools, new models, and new data sources can expand what an agent does without anyone updating its permissions.
| Stage | What happens | Governance question |
|---|---|---|
| Register | Owner, purpose, and scope are recorded | Who is accountable if this agent misbehaves? |
| Scope | Tools, data, models, and budget are assigned | What is the least access this task needs? |
| Test | Permission and policy checks run before go-live | Do the limits hold under realistic requests? |
| Deploy | Identity-bound access goes live | Is every action attributable to a user and agent? |
| Monitor | Traces, spend, and policy events are tracked | Is behavior still within the approved scope? |
| Revalidate after change | New tools, models, or data sources trigger a re-score | Has the Agent Authority Matrix score moved? |
| Detect drift | Access or spend growth is compared to the baseline | Is authority expanding without a decision? |
| Retire | Access is revoked, integrations are disabled, records are kept | Can this agent still act anywhere? |
Drift rarely shows up as a dramatic failure. It usually looks like an agent that quietly gained one more connector, one more data source, and a larger model over six months, without anyone re-scoring it.
Who owns AI agent governance: a RACI model
Agent governance fails most often at handoffs between teams. A RACI (Responsible, Accountable, Consulted, Informed) makes ownership explicit before the first incident, not during it.
| Activity | CISO / Compliance | CIO / CTO / CFO | COO / LOB Head | Platform Engineering |
|---|---|---|---|---|
| Approve new agents | A | C | R | C |
| Define governance policies | A | C | C | R |
| Set budgets and quotas | I | A | R | C |
| Monitor usage and spend | I | A | R | C |
| Approve high-risk actions | C | I | A | R |
| Respond to incidents | A | I | C | R |
| Produce audit evidence | A | I | I | R |
| Retire agents | C | I | A | R |
The pattern that works in practice is simple:
- Department heads manage local quotas, caps, and model access for their own teams.
- Risk and executive leadership see org-wide spend, policy events, and traces.
- IT and security own central policy and the agent registry.
Adapt the cells to your structure, but make sure every row has exactly one A. Organizations designing this operating model from scratch often start with AI governance consulting before choosing tooling.
Regulations and standards shaping agent governance
Few AI laws mention agents by name, but their logging, oversight, and risk-assessment duties apply directly to agent behavior. Several key dates moved in 2026, so older guidance often cites deadlines that no longer apply.
| Framework | Current status (verified September 2026) | What it means for agents |
|---|---|---|
| EU AI Act | High-risk obligations apply from December 2, 2027, for Annex III systems and August 2, 2028, for Annex I systems | Risk management, logging, human oversight, and documentation for agents used in high-risk areas such as hiring and credit |
| NIST AI RMF | Voluntary US framework built on Govern, Map, Measure, and Manage | A structure for assigning ownership, mapping agent context, and tracking risk over time |
| ISO/IEC 42001 | Certifiable standard for AI management systems | Documented processes, risk assessments, and monitoring evidence; certification applies to the organization, not a product |
| Colorado AI Act | Amended by SB 26-189, effective January 1, 2027, subject to attorney general rulemaking | Narrowed to disclosure and transparency for automated decision-making tools |
| GCC data protection rules | Saudi Arabia's Personal Data Protection Law, overseen by SDAIA, alongside SDAIA's AI guidance | Controls over where personal data goes when agents send it to external models |
The EU's Regulation (EU) 2026/1744, in force since July 27, 2026, pushed high-risk deadlines to December 2, 2027 (Annex III) and August 2, 2028 (Annex I). Colorado's SB 189 delayed its AI Act to January 1, 2027 and narrowed it to disclosure and transparency duties.
Governance software doesn't make you compliant, but it produces the evidence auditors ask for: identity-attributed logs, policy records, and oversight trails. See the guide to AI governance and compliance readiness for the full process.
How to evaluate AI agent governance software solutions
Most vendors describe similar features, so the useful test is what they can demonstrate. Ask each one to show these capabilities on your own sample requests rather than in a slide.
- Inline or after the fact: Ask whether the product decides before an action runs or only alerts after it. An alert on an executed payment is not governance.
- Runtime or documentation only: Confirm the product enforces policy on live requests. Documentation-only platforms need a separate enforcement tool alongside them.
- Third-party agent coverage: Check that agents from outside vendors, not only agents built in-house, can be registered and governed through the same controls.
- Revalidation on change: Ask how the product detects a new tool, model or data source on an existing agent and prompts a review.
- Deployment location: Confirm whether prompts and logs stay inside your own cloud tenant or pass through vendor infrastructure, which raises data residency questions.
- Model coverage: Verify the product works across the model providers you use today and can add new ones without re-engineering.
- Cost controls: Look for model routing, spend caps, and quotas by department and user, not just a monthly usage report.
- Audit-ready evidence: Request a sample trace. It should be identity-attributed and structured enough for an auditor to use without reformatting.
- Time to value: Ask how long it takes from contract signature to the first governed production request, not merely to login access.
- Pricing model: Understand whether pricing follows seats, agents, requests, or platform license, and how it scales as agent count grows.
Questions each buyer should ask
- CISO / Compliance: What evidence can I show auditors for any single agent action?
- CIO / CTO / CFO: What does governance cost to run, and what spend does it remove?
- COO / LOB Head: Can my team see its own usage and quotas without filing an IT ticket?
- Platform Engineering: How do existing agents plug in, and how much code has to change?
Test these checks on your own agents
Bring your agent list, your cloud requirements, and your frameworks, and see how governance performs on real requests before you buy.
AI Guardian vs other AI agent governance approaches: build, buy or extend
Free open-source toolkits now exist, so buyers reasonably ask why they should pay for governance at all. The answer depends on engineering capacity, how many agent stacks you run, and how quickly controls need to be live.
Microsoft released its Agent Governance Toolkit as an open-source project under the MIT license, and says it is the first toolkit to address all 10 OWASP agentic AI risks. Toolkits like this give strong building blocks, but they leave hosting, integration, dashboards, audit reporting, and ongoing maintenance to your team.
| Approach | Best for | Inline enforcement | Trade-off |
|---|---|---|---|
| AI Guardian | Teams needing runtime controls across models, vendors and departments | Yes, on every request | Live in 4 to 5 days after sign-off; pricing is quoted to scope |
| Open-source toolkits | Teams with a dedicated platform group and one agent stack | Yes, once built and hosted | Your team owns engineering, hosting and upkeep; months to go live |
| Cloud-native agent tools | Organizations running agents on a single cloud | Varies | Weak coverage for agents on other clouds or vendors |
| GRC documentation platforms | Compliance teams managing assessments and policy | Rarely | Strong on documentation, little runtime control |
| Agent security tools | Security teams focused on threats and attacks | Varies | Limited cost control and department-level visibility |
Decision guide:
- Build when you have a dedicated platform team, a single agent framework, and no deadline pressure.
- Buy when agents span several teams, models, and vendors, and auditors need evidence this quarter.
- Blend: Many teams buy the runtime layer and build only the integrations specific to their own systems.
Governance that pays for itself
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
Governance is usually budgeted as pure cost. Agent spend changes that math, because the same control layer that enforces policy can also decide which model handles each request.
Where agent spend leaks
- Premium models for simple tasks: Classification, extraction, and routine drafting often run on the most expensive model simply because it was the default.
- Uncapped usage: Looping or retrying agents consume tokens continuously, and without quotas nobody notices until the invoice arrives.
- Duplicate agents: Different teams build near-identical agents, each paying separately for the same model calls and integrations.
How routing and caps change the math
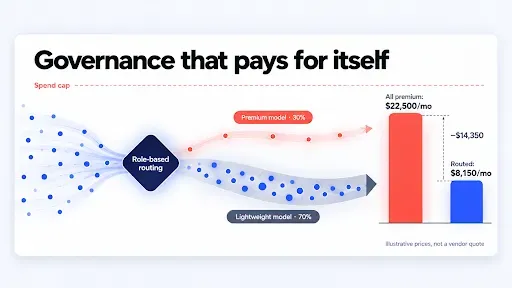
Role-based model routing sends routine work like classification and summaries to lightweight models and keeps premium models for complex reasoning, while department and user spend caps stop overruns before they happen. At an assumed one million requests a month, moving 70% of traffic to a lightweight model could cut costs from about $22,500 to $8,150 (illustrative prices, not a vendor quote).
- All premium: Sending every request to the premium model costs about $22,500 a month.
- Routed: Moving 70% of that traffic to the lightweight model, and keeping only 30% on premium, brings the bill to roughly $8,150. That saves about $14,350 a month.
The routing split should come from quality testing on real tasks, not guesswork, and the numbers should be rerun with your providers' current list prices. At meaningful volume, routing alone can cover a large share of what the governance layer costs.
Meet AI Guardian: AI agent governance software
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
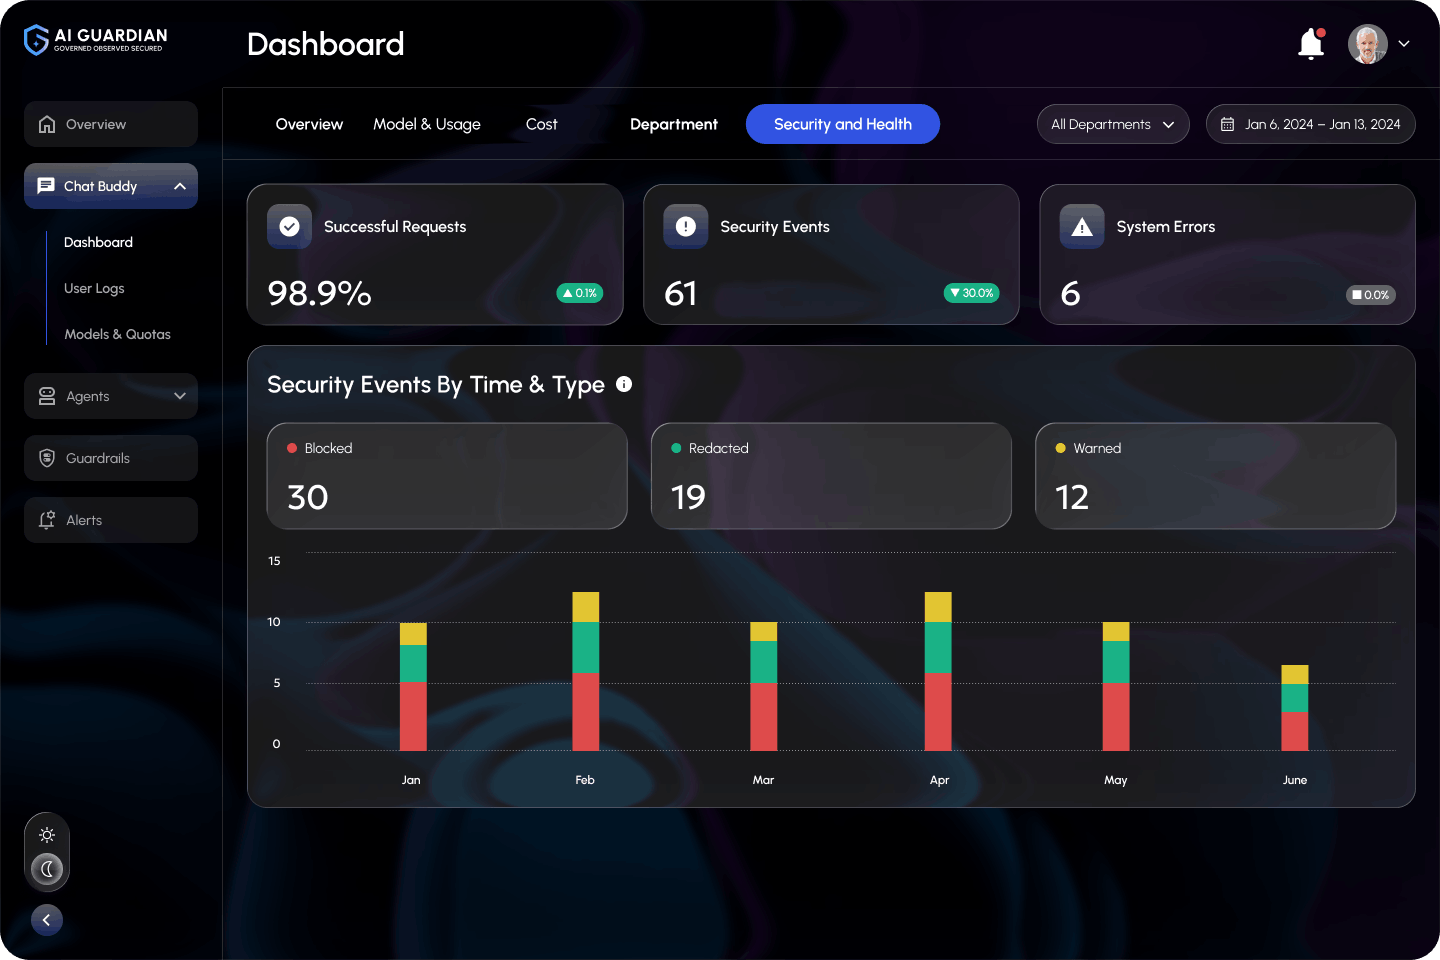
Measured against the evaluation criteria above, this is where AI Guardian fits. AI Guardian is Folio3's AI governance control plane. It sits between people, agents, and models, so every request passes the same identity, data, policy, and cost checks.
- Agent registry: Custom and third-party agents register centrally with an owner and scope, delivering the inventory pillar before any agent reaches production.
- Identity inheritance: Each agent acts under the user's SSO identity and role-based permissions, delivering the identity pillar without separate standing agent credentials.
- PII and document redaction: Personal data and identifiers are masked in prompts and multi-page files before any model receives them, delivering the data protection pillar.
- Off-domain enforcement: Requests outside an agent's defined domain are declined based on context, delivering the policy pillar at runtime rather than in reports.
- Role-based model routing: Each workload goes to the cost-fit model for the user's role and task, delivering the model governance pillar.
- Spend caps and quotas: Department and user limits stop overruns before they happen, turning cost governance into an operating control.
- Multi-agent orchestration: Agents that hand work to each other stay inside the same governed path, so every handoff keeps identity and policy attached.
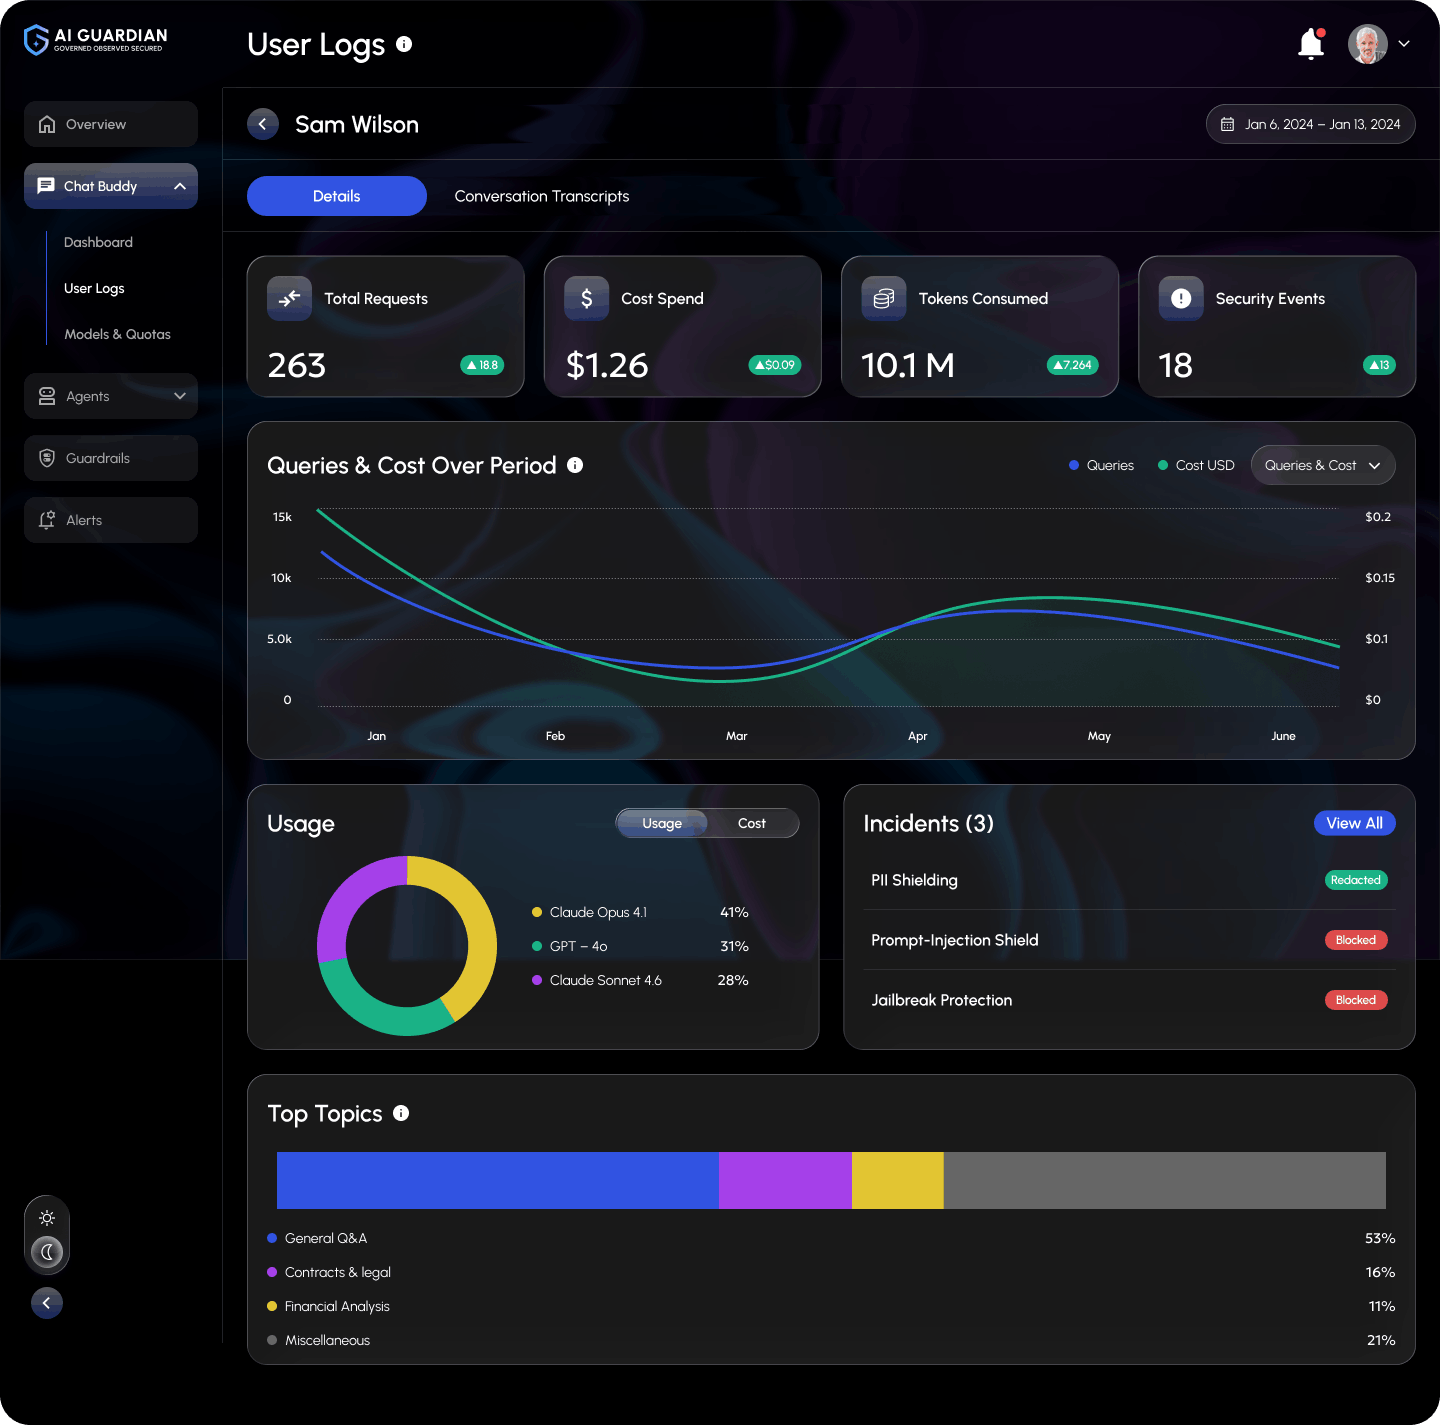
- Identity-attributed audit trails: Every request records user, agent, policy decision, model, tokens, and cost, delivering the evidence pillar in a structured form.
- Executive and LOB dashboards: Department heads see their own usage and quotas while risk leaders see org-wide spend and policy events.
AI Guardian deploys inside your own Azure, AWS, or GCP tenant, so prompts and logs stay in your environment. It is also listed on the Microsoft Marketplace. It governs requests at runtime. It does not replace model-level bias testing or drift monitoring, which belong in MLOps tooling alongside it.
One governed path for every agent request
See the AI Guardian product page or view the Microsoft Marketplace listing.
How AI Guardian governs every agent request
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
Every request, whether it comes from a person in Teams or from an agent calling another agent, follows the same five steps. This sequence is what turns written policy into enforced policy.
- Verify user and agent identity: SSO confirms who is asking and which registered agent is acting, then loads the matching role and policy set.
- Inspect data before egress: Prompts and attachments are scanned, and sensitive values are masked before anything leaves your tenant.
- Enforce policy and route: Off-domain requests are declined; allowed requests go to the approved model for that role and remaining quota.
- Execute governed agent actions: The agent completes its task within its registered scope, and any handoffs stay inside the same governed path.
- Log evidence and cost: The request is recorded with identity, policy decision, model, tokens, and cost for audit and chargeback.
Inline enforcement: why governance must sit in the request path
Tools that watch agents from the side can only alert after an action has run. By then, the payment is sent, the record is changed, or the data has left.
Inline enforcement evaluates each request before execution, which is the only point where "no" still prevents anything. AI Guardian sits in that path between the user or agent and the model, so the policy decision happens first and the evidence is written at the same moment.
Expert insight
“Most teams I work with already have an AI policy. What they don't have is a way to enforce it once an agent starts acting on its own at two in the morning. A policy document can't stop an agent from calling the wrong API or sending customer data to an external model. A control in the request path can. The programs that hold up in production treat governance as part of how the agent runs, not a review that happens after something goes wrong.”
AI Guardian vs other AI agent governance software approaches
The table compares categories rather than named vendors, because products within each category vary. Use it to identify which layer matches your biggest gap.
| Capability | Open-source toolkits | GRC documentation platforms | Agent security tools | Developer AI gateways | AI Guardian |
|---|---|---|---|---|---|
| Runtime enforcement | Yes, once built and hosted | Limited | Threat-focused | Yes | Yes |
| Inline, before-action enforcement | Depends on implementation | Rarely | Varies | Yes | Yes |
| Employee workspace included | No | No | No | No | Yes (Teams, Slack, web, mobile) |
| File-level PII redaction | Build it yourself | No | Varies | Varies | Yes |
| Cost and model governance | Build it yourself | No | Rarely | Yes | Yes, with department quotas |
| Multi-agent orchestration | Framework-dependent | No | No | Limited | Yes |
| Deploys in your cloud | Yes | Usually vendor SaaS | Varies | Varies | Yes |
| Engineering effort to run | High | Low | Medium | Medium | Low; implementation included |
| Time to go live | Months | Weeks | Weeks | Days to weeks | 4 to 5 days after requirements sign-off |
| Public pricing | Free license | Rarely | Rarely | Often | Quoted to scope |
From kickoff to governed agents in days
AI Guardian comes with a structured implementation engagement, not only a platform login. Once the Phase 1 blueprint is signed off, configuration and deployment take four to five business days, depending on the environment.
Phase 1: Requirements and alignment (2 to 4 hour sessions)
- Review AI policies and regulations: Existing policies and applicable frameworks are mapped so controls reflect your actual obligations, not generic templates.
- Map LOBs and use cases: Each line of business and its priority agent use cases are documented with owners and data types involved.
- Define guardrails and model access: Redaction rules, domain boundaries, and approved model tiers are agreed for each role and department.
- Set budgets and ownership: Department quotas, spend caps, and accountable owners are assigned using the RACI model before configuration begins.
- Score existing agents on the Agent Authority Matrix: Each agent in use receives a tier, which determines its approval rules and review frequency.
Phase 2: Configure, deploy, go live (4 to 5 business days)
- Configure hierarchy and policies: Organization structure, roles, guardrails, and quotas are set up to match the signed-off blueprint.
- Register existing agents: Custom and third-party agents are added to the registry with owners, scopes, and their matrix tier.
- Deploy inside your tenant: The platform is installed in your Azure, AWS, or GCP environment, keeping prompts and logs in your control.
- Smoke test and hand over: Real request types are tested against policies before go-live, followed by handover to named owners.
Timelines vary with the number of integrations and the target environment.
Why teams choose Folio3 AI for agent governance
AI Guardian is built by a team that also builds production agents for clients, so its controls reflect how agents behave in real deployments rather than in demos.
- 20+ years of engineering: Folio3 has delivered enterprise solutions for over two decades across the US, GCC, and other markets.
- 950+ projects delivered worldwide: Delivery experience spans data, AI, and application projects for organizations of different sizes and regulatory profiles.
- ISO 27001 certified company: The certification covers Folio3's information security management system; it is a company credential, not a certification of the AI Guardian product.
- Listed on Microsoft Marketplace: Azure customers can find and procure AI Guardian through Microsoft Marketplace alongside their existing cloud agreements.
- Builds and governs agents: The same engineering organization delivers custom AI agent development and governs those agents, so governance design reflects real agent behavior.
- US and GCC presence: Teams in the US and GCC support rollouts where data protection rules such as Saudi PDPL shape deployment choices.
Give every AI agent a governed path to production
Agents will keep multiplying across your teams, and each new one adds tools, data, and spend to govern. Start by registering every agent and scoring it on the Agent Authority Matrix. Next, put identity, redaction, and policy in the request path. Then assign one accountable owner per activity. AI Guardian gives each agent an identity, a policy, a budget, and an audit trail, deployed inside your cloud in days.
Bring your agents, frameworks, and cloud environment
Book a consultation built around your agent inventory, risk tiers, and cloud tenant, and see redaction, routing, and audit traces on sample requests.
Frequently asked questions
What is an AI agent governance solution?
It is software that controls what autonomous AI agents may do, covering identity, tool access, data protection, model choice, spend, and audit logging. The best solutions enforce these controls on each request at runtime instead of documenting them afterward.
How is AI agent governance different from AI governance?
AI governance focuses on model outputs, bias, and acceptable use, while agent governance adds control over actions, tool calls, and handoffs between agents. The unit being governed shifts from a single answer to a chain of actions.
What is the difference between agent AI security and governance?
Security protects agents from attackers, such as prompt injection and compromised credentials, while governance defines and proves what legitimate agent behavior looks like. Both rely on agent identity, policy decisions, and audit logs, so many teams run them through one control layer.
What features should AI agent governance software include?
Look for an agent registry, identity inheritance, PII redaction, policy enforcement, model routing, spend caps, and identity-attributed audit trails. The most important test is whether it enforces inline before an action runs, rather than alerting afterward.
Can AI Guardian govern agents we already built or purchased?
Yes, custom and third-party agents can be registered and routed through AI Guardian's governed path. Each one then inherits the same identity, redaction, spend and audit controls as any other request.
Why not build agent governance with an open-source toolkit?
Open-source toolkits provide useful building blocks, but your team then owns hosting, integration, dashboards, audit reporting, and ongoing maintenance. They suit organizations with a dedicated platform team; a governance platform suits teams that need controls across many agents within weeks.
Does AI Guardian run inside our own cloud?
Yes, AI Guardian deploys inside your own Azure, AWS, or GCP tenant. Prompts and logs stay within your environment.
How does AI agent governance support EU AI Act and NIST AI RMF requirements?
Governance software produces the logs, oversight records, and policy evidence that these frameworks ask for, such as record-keeping and human oversight. It supports compliance work but does not certify or make a system compliant on its own.
How long does it take to deploy AI agent governance software?
It depends on the approach: open-source builds can take months, while AI Guardian goes live in four to five business days after requirements sign-off. Integration count and the target environment affect the timeline.
How much do AI agent governance software solutions cost?
Cost depends on the number of agents and users, the deployment model, integrations, and whether implementation is included. AI Guardian is priced as an implementation engagement plus a platform license, quoted to your scope.
Which teams should own AI agent governance?
Ownership is shared: security and compliance usually hold accountability for policy, line-of-business heads own their agents and quotas, and platform engineering runs the controls. A RACI with exactly one accountable owner per activity prevents gaps between teams.
Related reading
- AI Governance Maturity Model: How to Assess and Improve
- AI Governance and Compliance Readiness: A Practical Guide
- AI Guardian product page
Written by the Folio3 AI Editorial Team. Technical content on frameworks, regulation, and agent controls was reviewed by Abdul Sami, Head of AI Development at Folio3 AI, in September 2026.

